
Know when your credentials leak.
Surface watches breach dumps, combolists and stealer logs for the domains it already discovered. When an employee address shows up exposed, you see it, acknowledge it and act on it, before someone else does.
- Breach & stealer-log monitoring
- Grouped by source
- Part of Surface
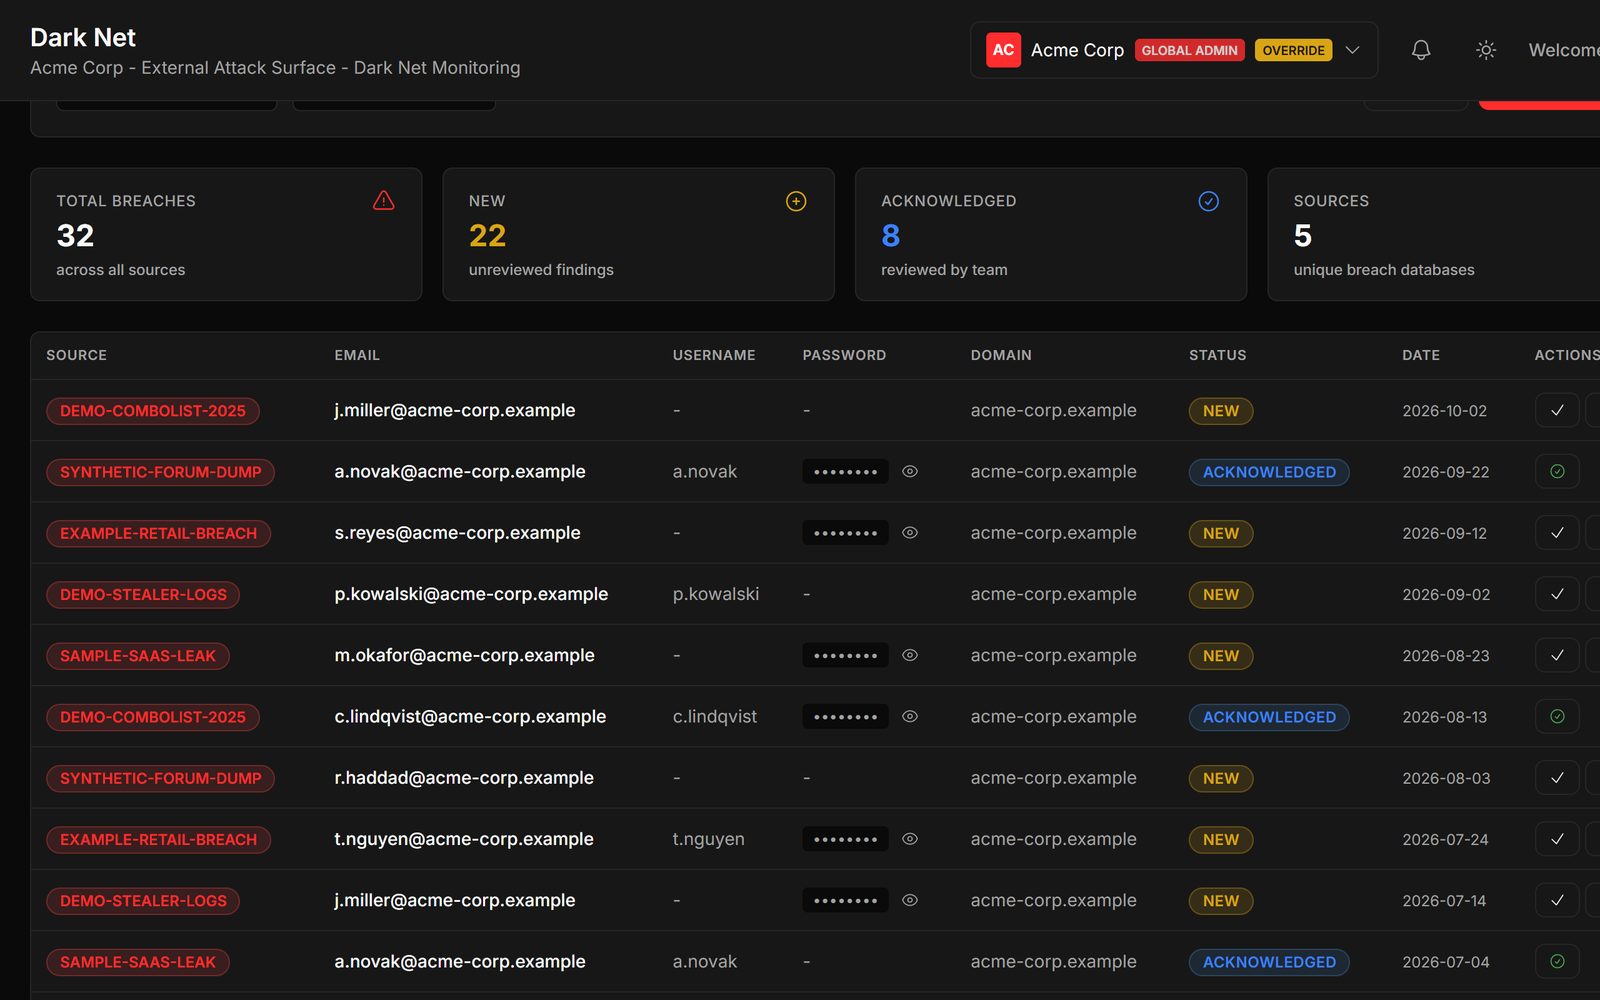 32 exposures across 5 sources
Caught early
The same email addresses your discovery finds also end up in breach dumps, combolists and stealer logs for sale on the dark web. A leaked password nobody noticed is an open door. Dark web monitoring closes the gap between a leak and your awareness of it.
Every exposure, in one place.
Breach and stealer-log matches for your domains, grouped by source and ready to acknowledge. Passwords are always masked.
Monthly findings · last 12 months
| Source | Username | Password | Status | Date | Action | |
|---|---|---|---|---|---|---|
| DEMO-COMBOLIST-2025 | [email protected] | — | — | New | 2026-10-02 | |
| SYNTHETIC-FORUM-DUMP | [email protected] | a.novak | •••••••• | Acknowledged | 2026-09-22 | |
| EXAMPLE-RETAIL-BREACH | [email protected] | — | •••••••• | New | 2026-09-12 | |
| DEMO-STEALER-LOGS | [email protected] | p.kowalski | — | New | 2026-09-02 | |
| SAMPLE-SAAS-LEAK | [email protected] | — | •••••••• | New | 2026-08-23 | |
| DEMO-COMBOLIST-2025 | [email protected] | c.lindqvist | •••••••• | Acknowledged | 2026-08-13 |
Where leaked credentials show up.
Dark web monitoring checks your domains against the places exposed credentials circulate, and groups every match by its source.
One thread, from your domain to your people.
Dark web monitoring isn’t a separate tool. It runs on the assets Surface already discovered, and feeds the same routing and training.
Pair it with brand & phishing protection.
Leaked credentials are one signal. The brand protection add-on watches for the other side of the attack: lookalike domains, typosquats and impersonation set up to phish your people and customers.
- Typosquats & homoglyphs: domains built to be mistaken for yours.
- Evidence capture: screenshots and infrastructure, correlated automatically.
- Takedown-ready cases: packaged so you can act fast.
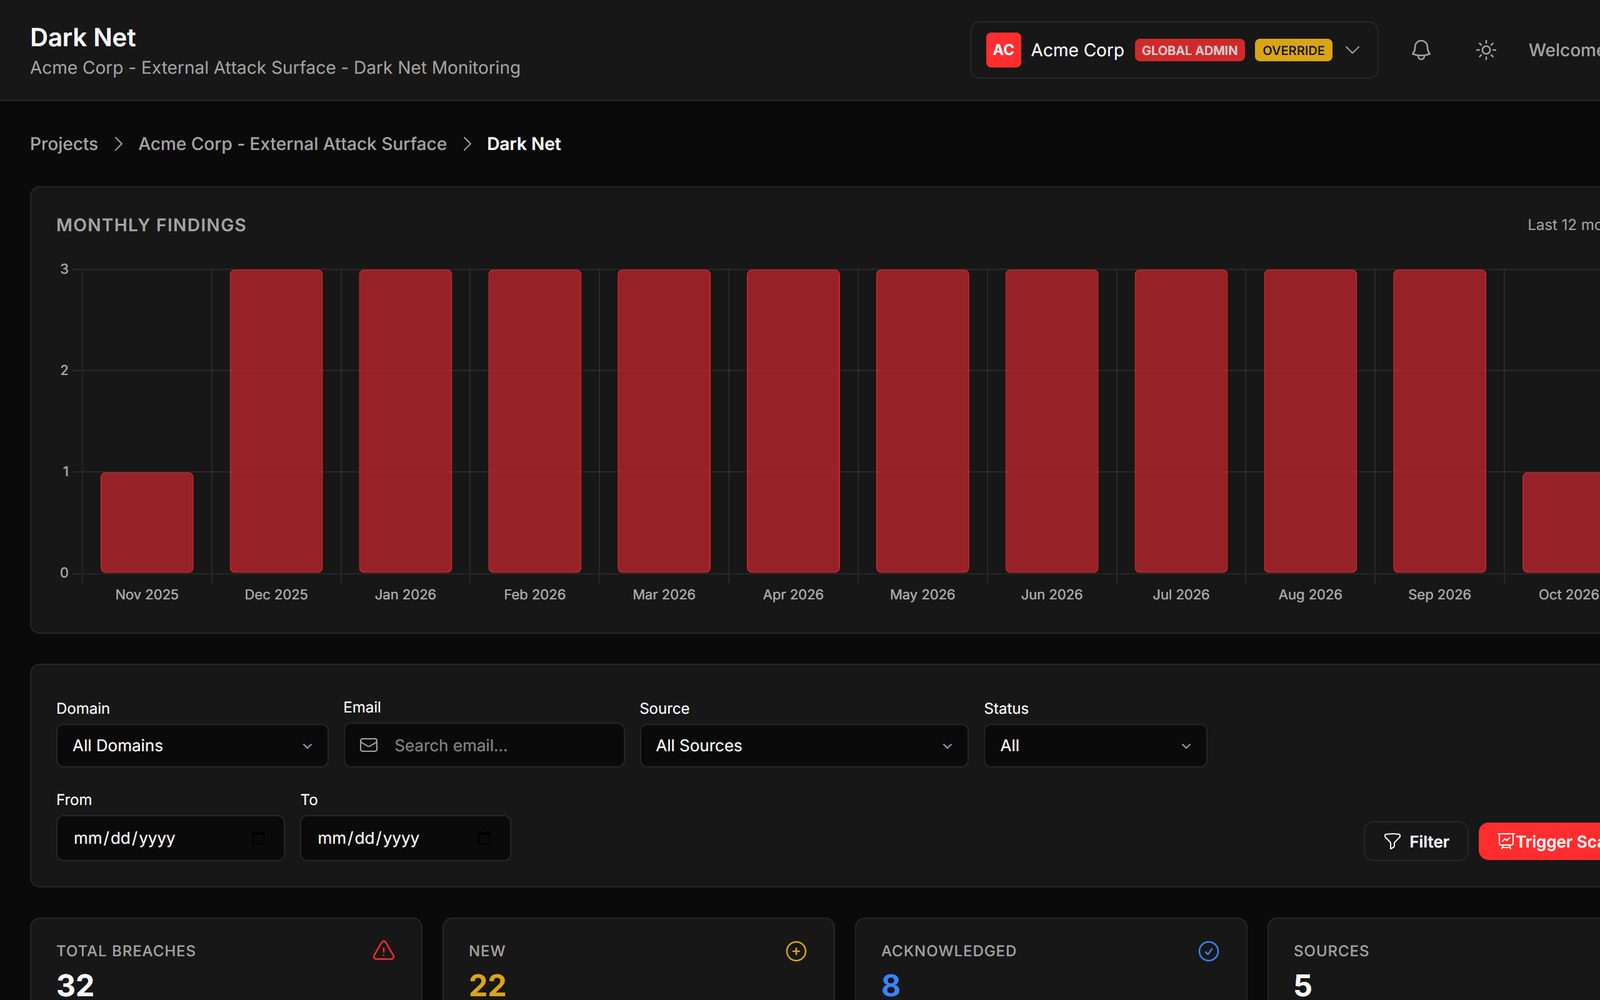 Monitored continuously
Questions about dark web monitoring?
If yours isn’t here, we’ll answer it in the demo.
What exactly is monitored?
The email addresses tied to the domains in your Surface scope, checked against breach dumps, combolists, stealer logs and known breach databases.
Do you show the leaked passwords?
No. Passwords are always masked. You see that an exposure exists, from which source and when, so you can force a reset.
Is it a separate product?
No. Dark web monitoring is part of Surface, running on the same assets and projects as discovery.
How do findings reach us?
Through the same integrations as the rest of Surface: Jira, Slack, Discord and email, with rules per event.
How often is it checked?
On the schedule you set, and you can trigger a scan on demand at any time.
Find the leaks before they're used.
See your exposed credentials the way an attacker shopping the dark web would, and shut the door first.