
One platform for exposure, human risk and awareness.
See what attackers see, test how your people respond, and train them against the attacks they will actually face. All in one environment.
- Agentless deployment
- Built in Europe
- Jira, Slack & SIEM ready
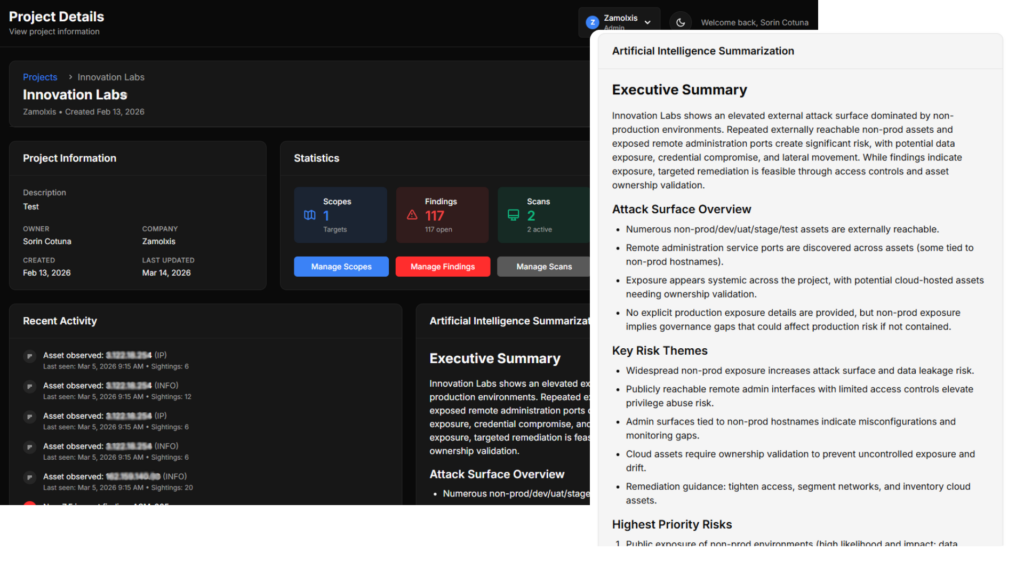
A unified security platform, not a collection of separate tools.
Security teams often juggle one tool for exposure visibility, another for phishing simulations and a separate system for awareness training. We bring these functions together, so you can understand risk, simulate attacker techniques and improve human resilience with less friction.
Attack Surface Management
Discover internet-facing assets and reduce the blind spots attackers may already see.
- External asset discovery
- Continuous monitoring
- Risk scoring and prioritization
- Asset graph explorer
- Dark web leak monitoring
- Alerts to Jira, Slack and Discord
Phishing Simulation
Run realistic simulations to test user behaviour in controlled, educational scenarios.
- Email phishing campaigns
- Smishing, vishing and quishing
- Targeted spear phishing
- 2FA and MFA bypass scenarios
- Templates, landing pages and tracking
- Bot-aware result filtering
Security Awareness Training
Interactive courses in a dedicated learner portal, assigned by your administrator.
- Dedicated learner portal
- Courses assigned by admins
- Attacks simulated in web emulators
- Bite-sized modules
- Explanations after every answer
- Progress and completion tracking
Most companies see only 10% of their risk. We reveal the rest.
Attackers target people as much as infrastructure. That is why exposure visibility, phishing simulation and training belong in one place.
of breaches exploit humans.
of their risk is all most companies can see.
Three capabilities. Built to work together.
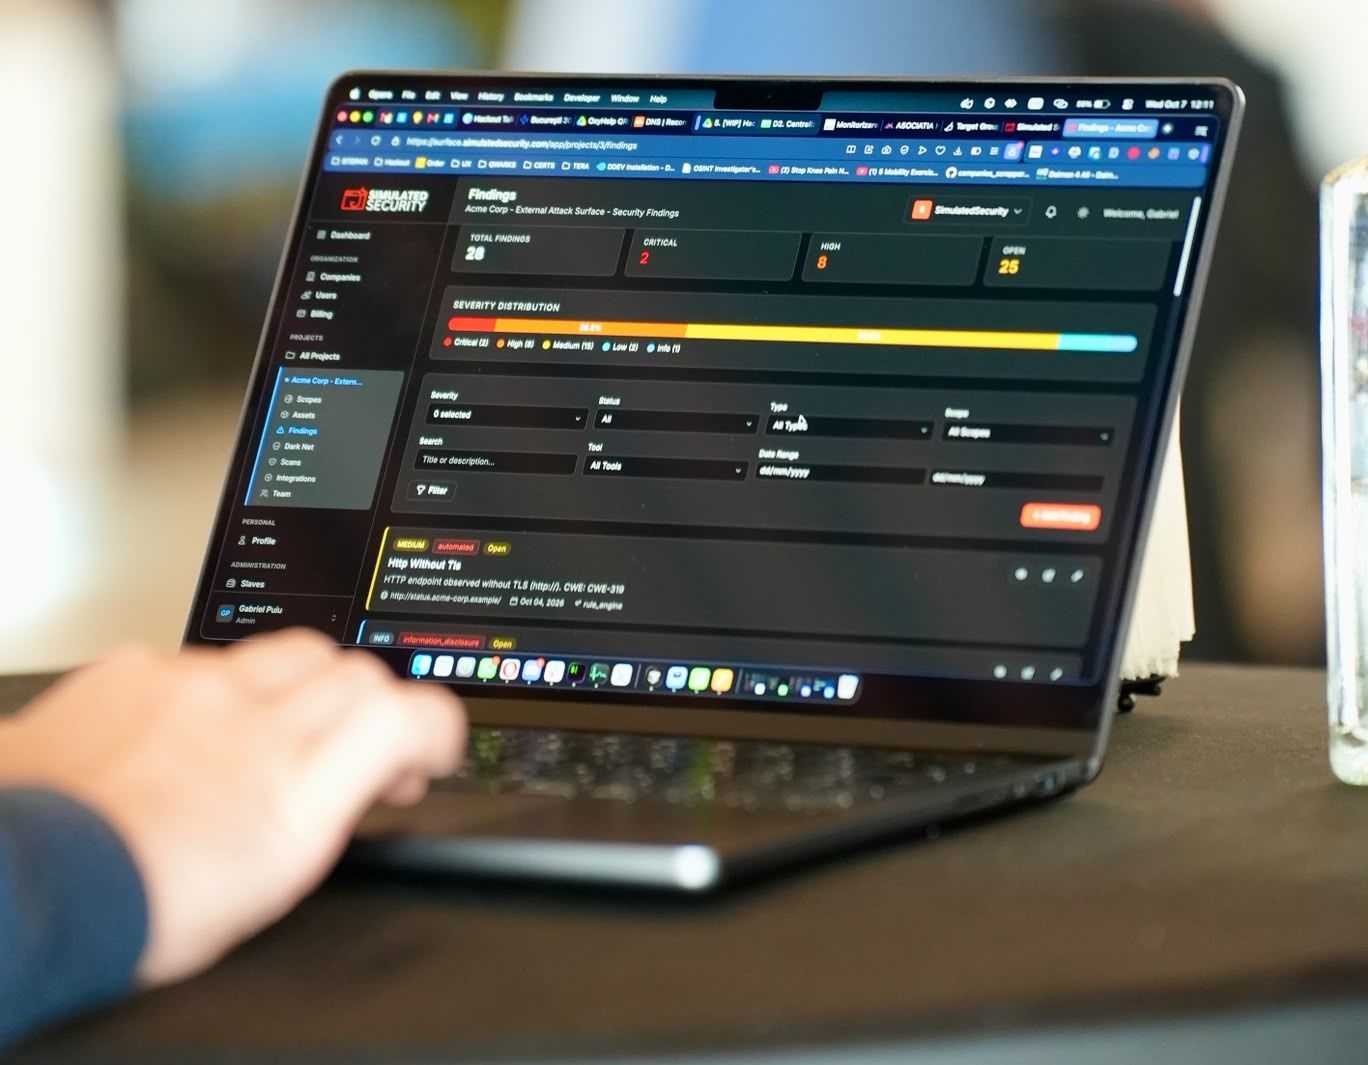
Understand what your organization exposes to the internet.
ASM identifies internet-facing assets and gives security teams a stronger foundation for ongoing visibility and prioritization.
- Agentless discovery: internet-facing assets mapped without installing anything on endpoints.
- Evidence-backed scoring: findings ranked by exposure, exploitability and ownership signals.
- Dark web monitoring: leaked credentials and compromised assets surfaced early.
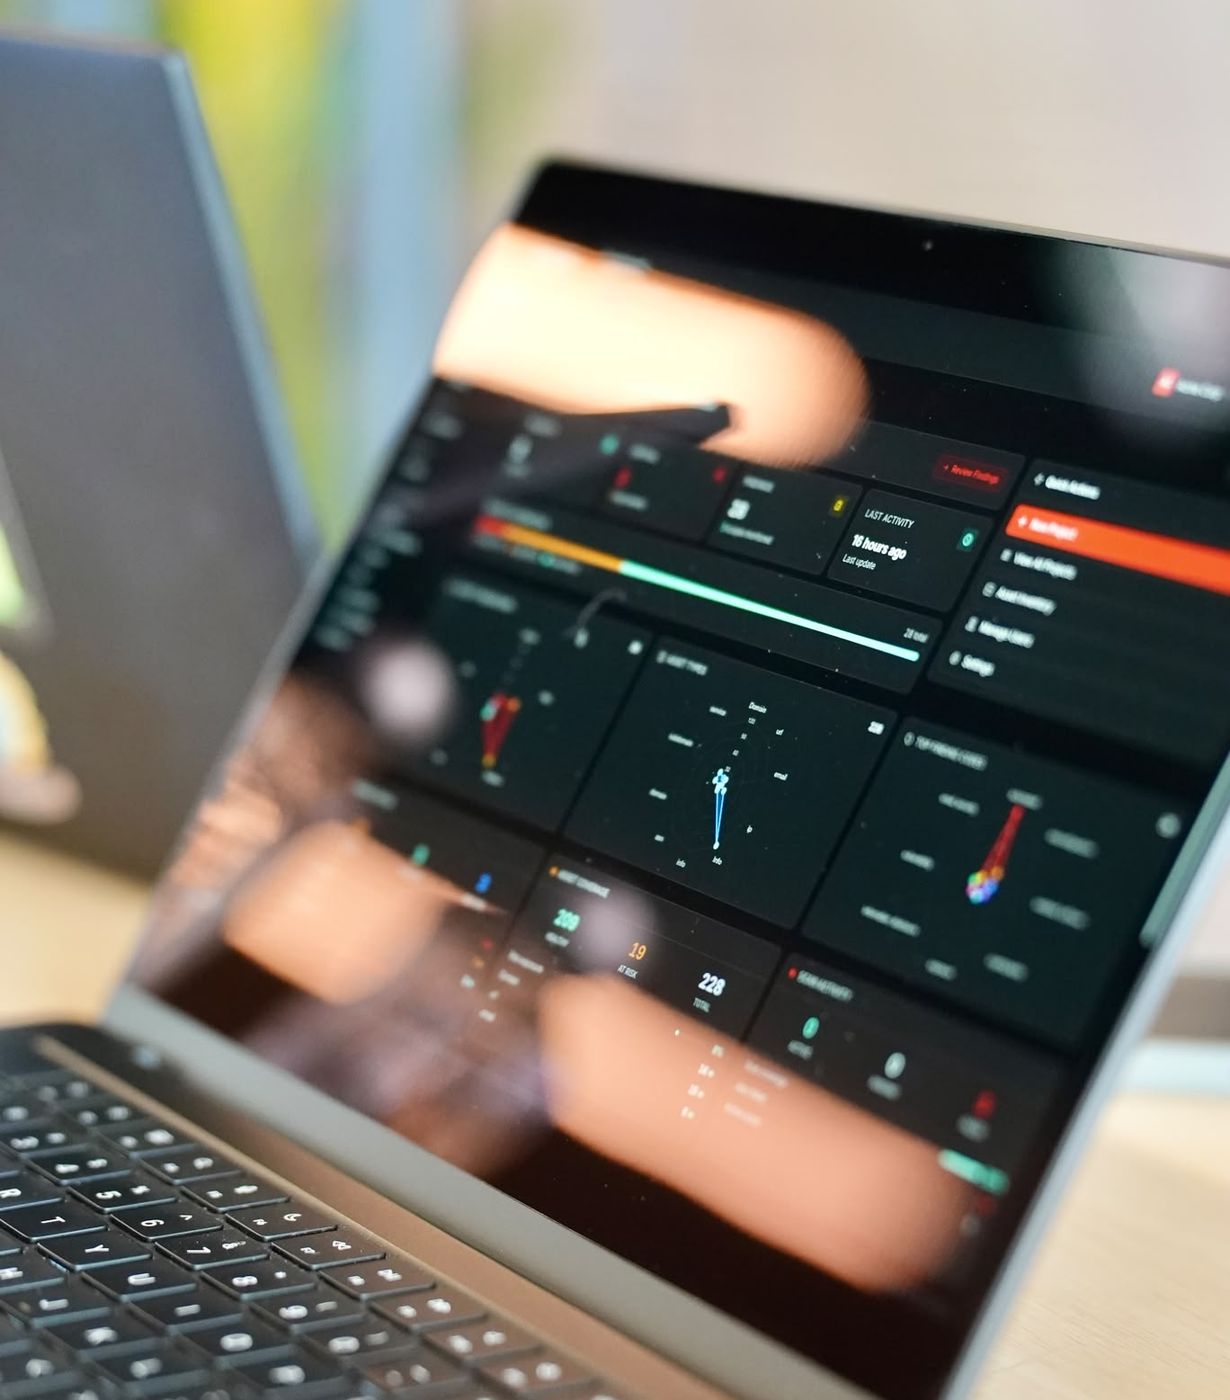 Continuous monitoring on
Simulate the attacks your people will actually face.
Create realistic campaigns across email, SMS-style flows, QR phishing and targeted spear phishing, built on real-world hacker techniques.
- Every channel: phishing, smishing, quishing, vishing and spear phishing.
- Realistic flows: templates, landing pages and 2FA / MFA bypass scenarios.
- Clean results: tracking with bot-aware controls, so reports reflect real behaviour.
 Automated campaigns
Training that goes beyond quizzes and theory.
Learners get a dedicated portal where they complete the courses assigned by their company administrator.
- Learner portal: every user sees exactly the courses assigned to them.
- Web emulators: real attacks simulated inside the course, with practical ways to spot them.
- Explanations after every answer: retention comes from understanding, not memorising.
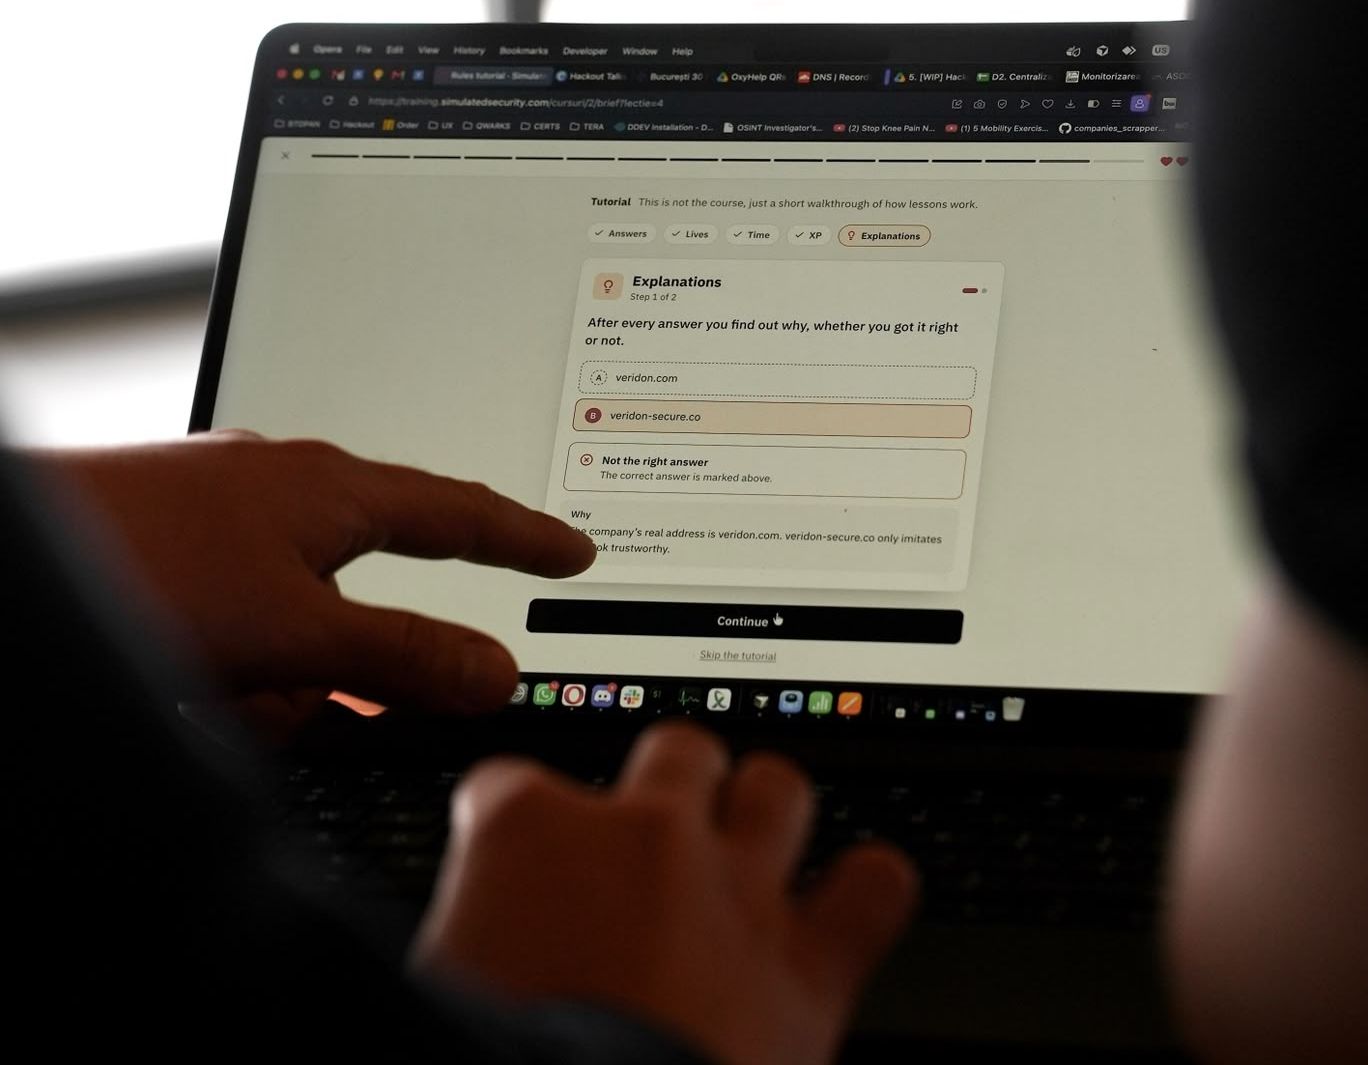 Dedicated learner portal
See risk. Simulate it. Reduce it.
Three capabilities, one continuous security story.
Each capability reinforces the others, so every cycle starts from a smaller attack surface.
Why organizations choose a unified platform.
Less tool sprawl
External visibility, phishing simulation and training in one environment.
Stronger workflows
Exposure discovery, human risk testing and awareness education, connected.
Operational clarity
Manage multiple security initiatives without unnecessary complexity.
Scalable adoption
Company-wide rollout, designed for both administrators and learners.
Findings land where your team already works.
Built-in connectors, webhooks and an API-first approach for routing.
See the platform in action.
A guided walkthrough of all three products, tailored to your environment.
Is this agentless?
Yes. Discovery and monitoring are designed to work without endpoint agents for fast deployment.
Can we integrate with Jira and SIEM?
Yes. Use built-in connectors, webhooks, and an API-first approach for routing.
How do you reduce noise?
Evidence-backed findings and scoring aligned to exposure, exploitability, and ownership signals.
Can we customize severity policies?
Yes. Map checks to your internal thresholds and enforce policies across business units.
Attacks are imminent. Are you ready?
Discover hidden weaknesses across your systems and team, simulate real-world threats, and train your staff.