Attack surface management

Full-Spectrum Operational Security

We continuously map, score and monitor every exposed asset, known and unknown, before adversaries can exploit them.

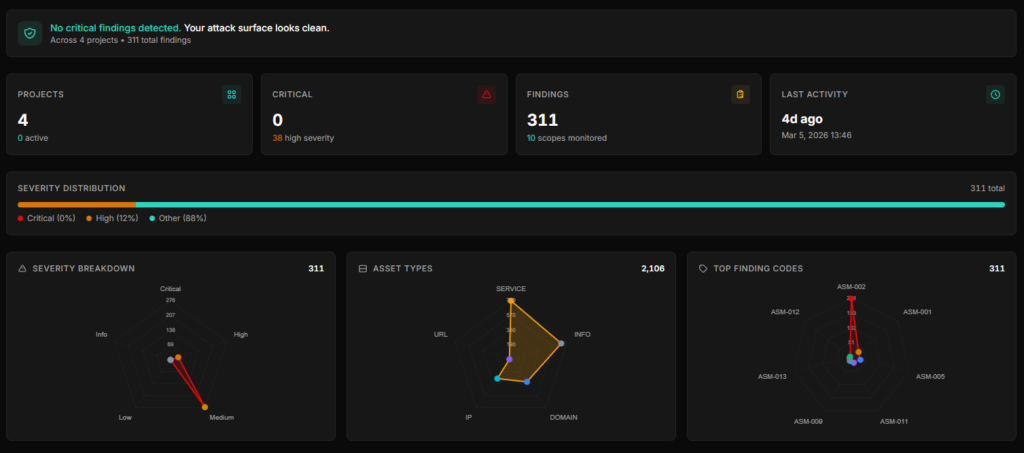
Attack surface dashboard with projects, findings and severity breakdown No critical findings detected Every exposed asset, scored
Trusted by

Operator-Tested.
Mission-Ready.

Built by security professionals. Military-grade, dual-use technology for teams that need an operational advantage.

Built in EuropeDual-use
4.9
★★★★★

Based on 9 Clutch reviews

Unified cyber command

See the platform in action.

Take full control over your human risk and attack surface from a single, uncompromising interface.

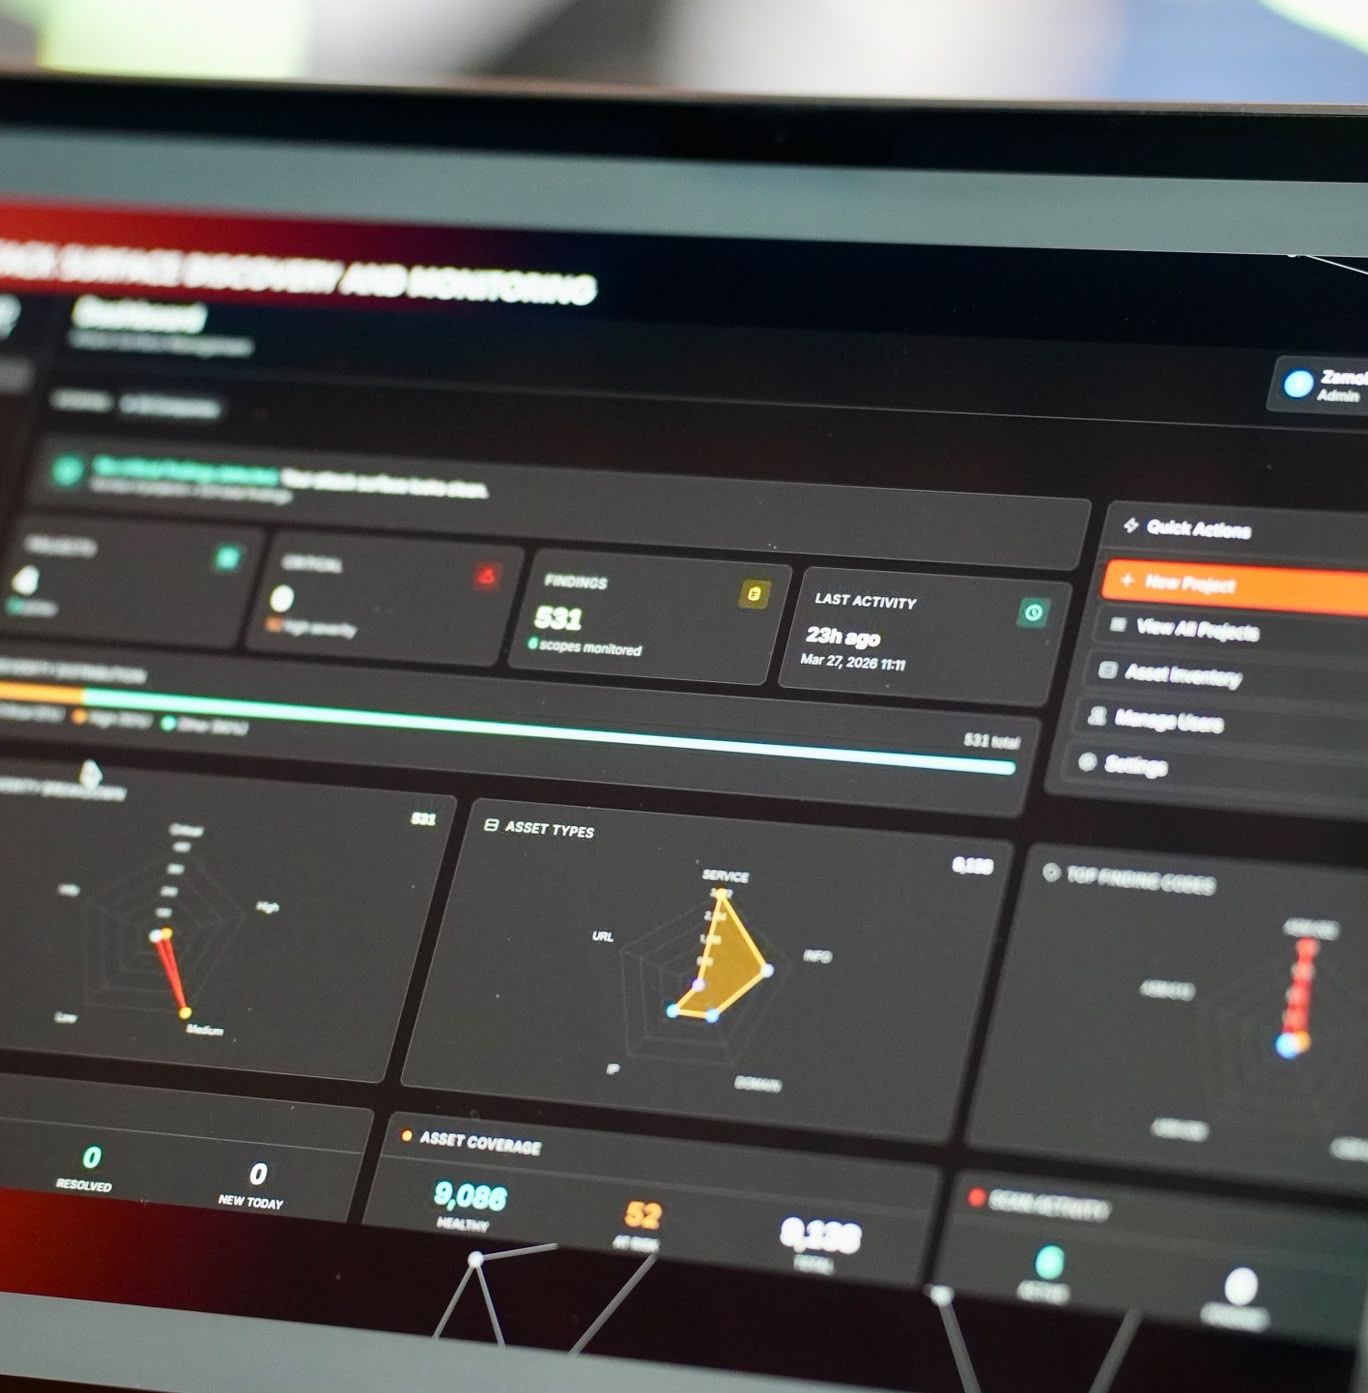
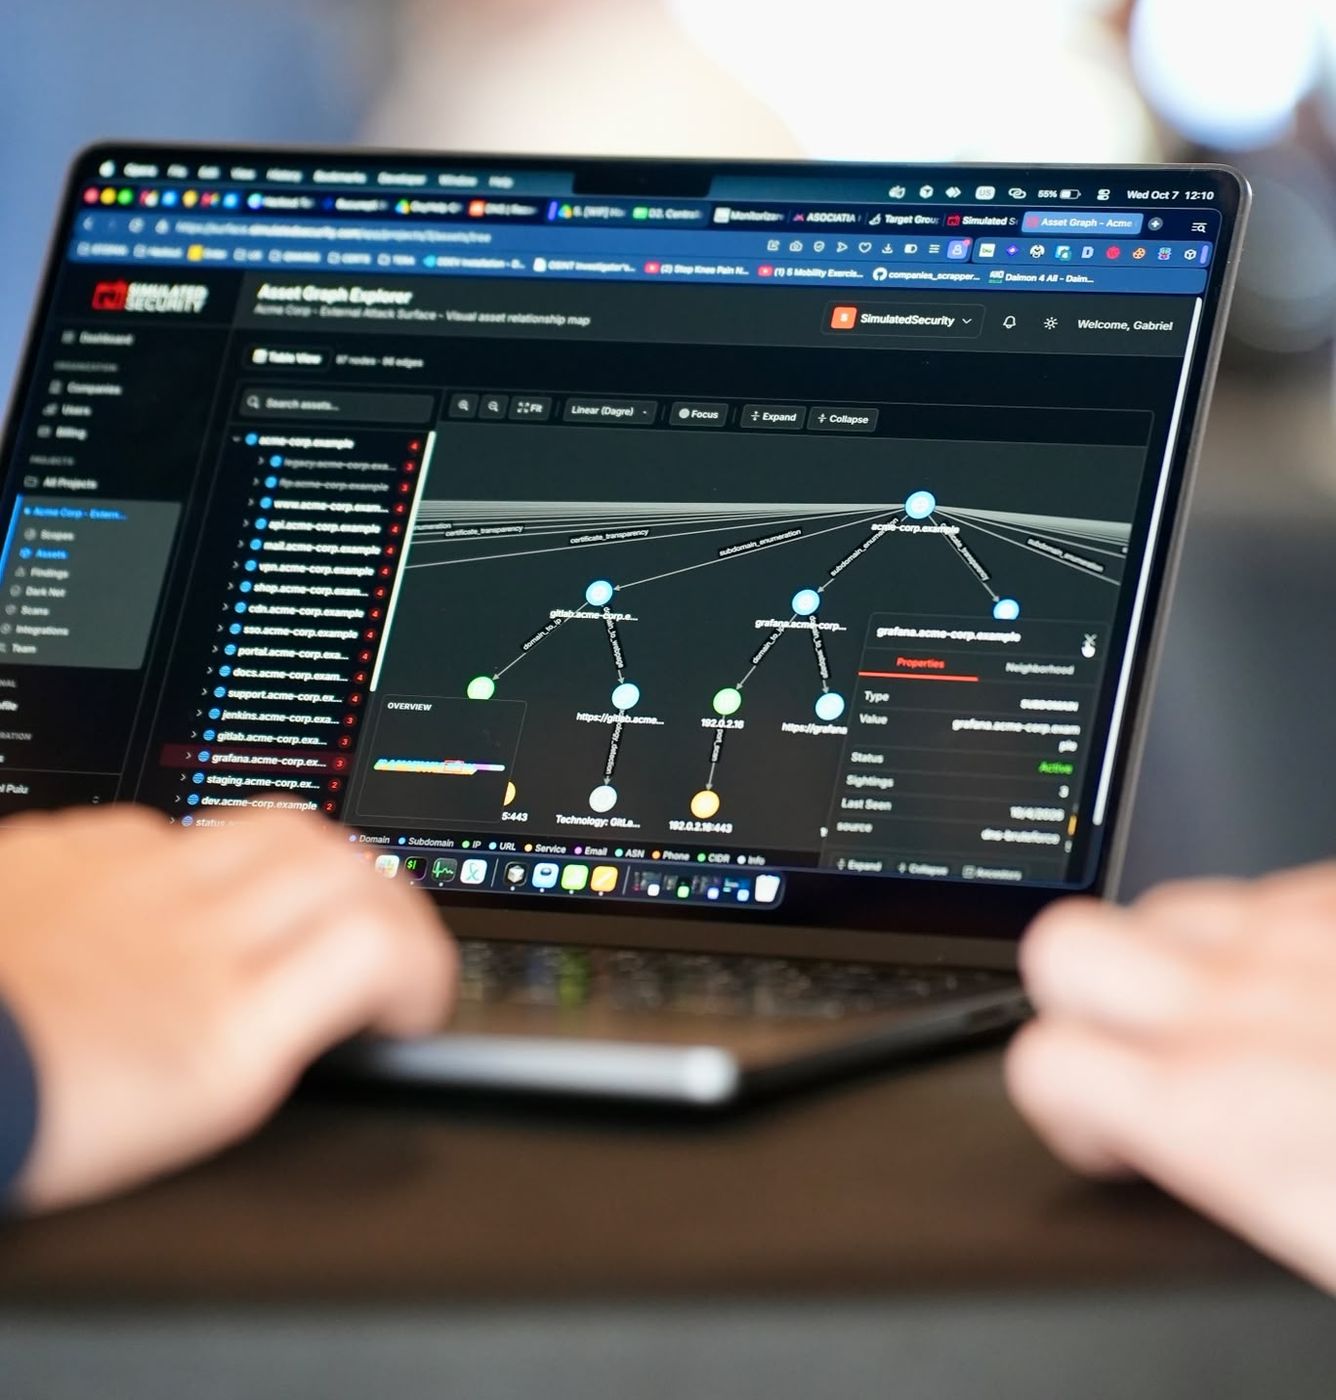
The attack surface dashboard running on a laptop
How the platform works

Three capabilities. One continuous security story.

Exploring an asset graph in the platform
01

Discover external exposure with ASM

Attack Surface Management improves visibility into what is exposed externally.

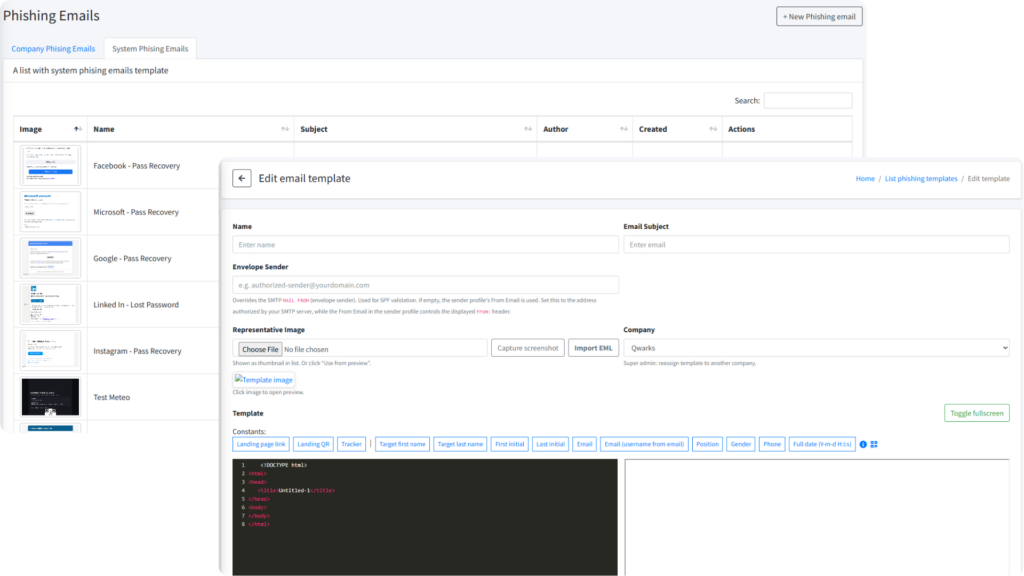
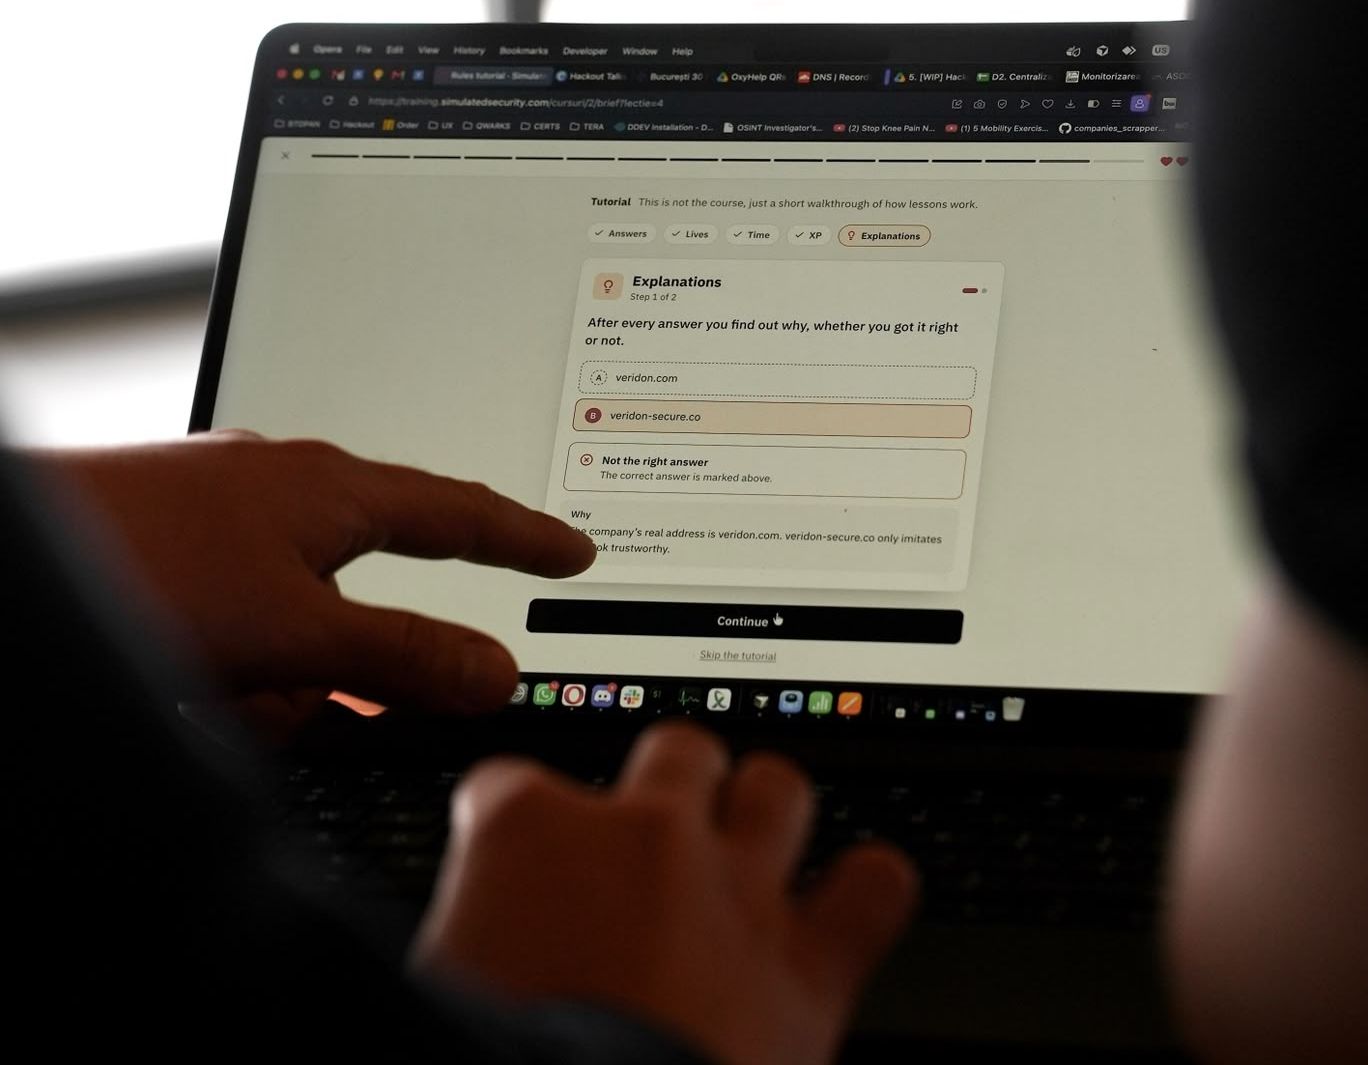
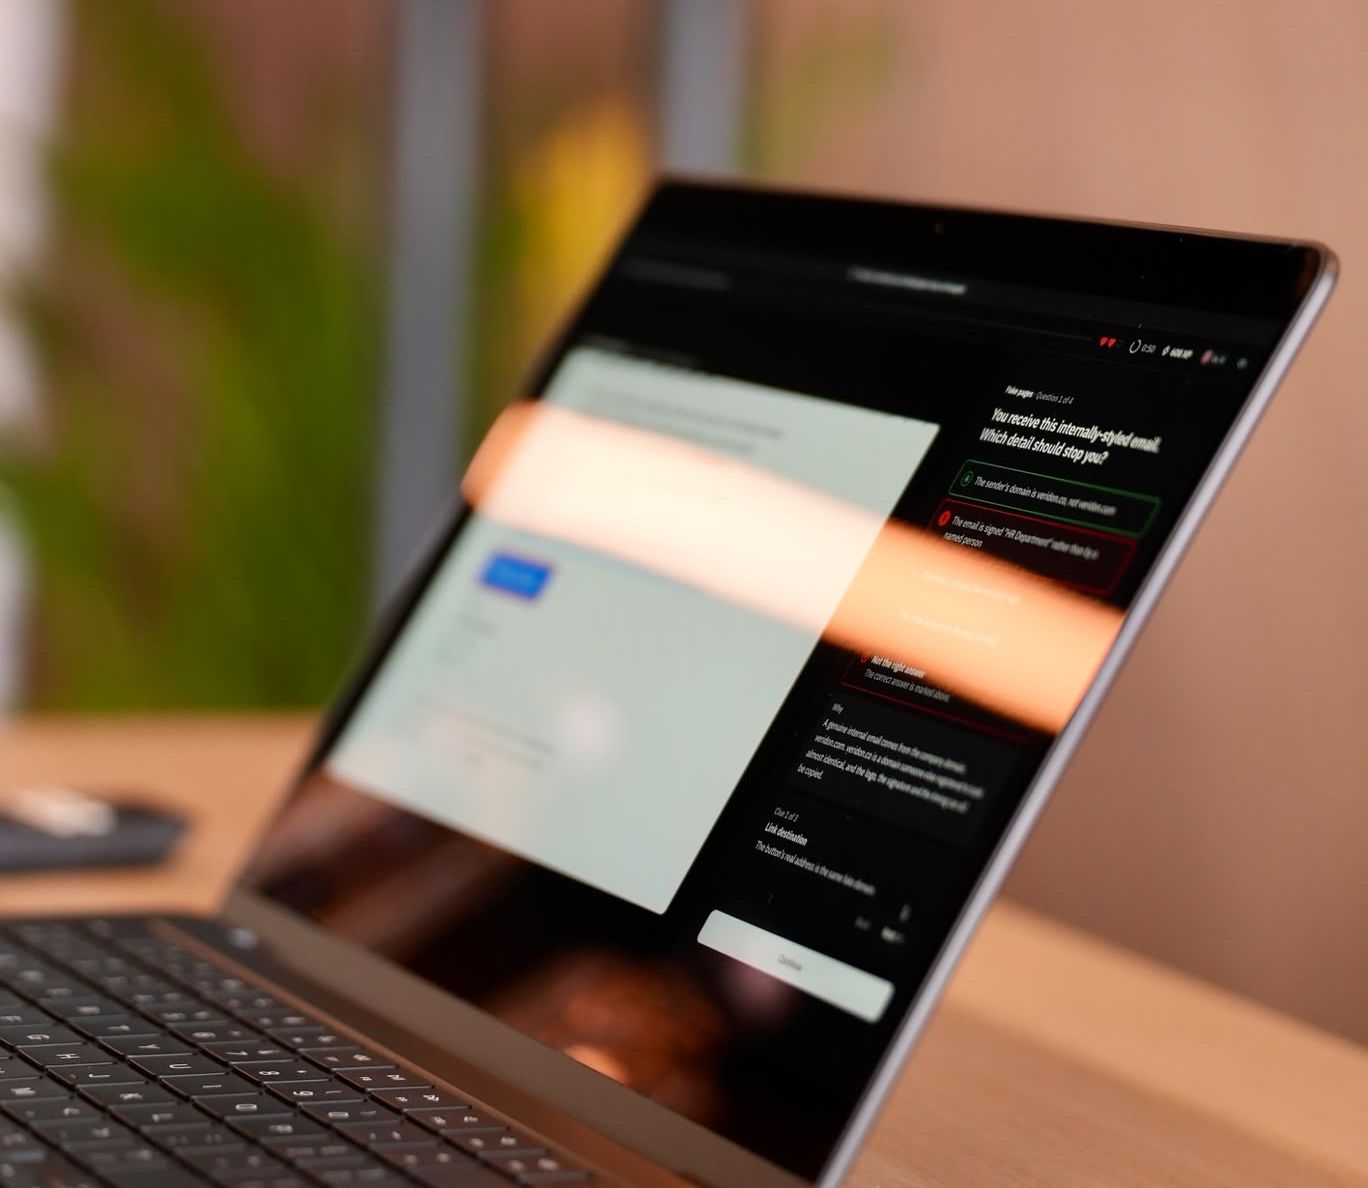
A phishing simulation open on a laptop
02

Test human risk with phishing simulations

See how users respond to realistic social engineering scenarios.

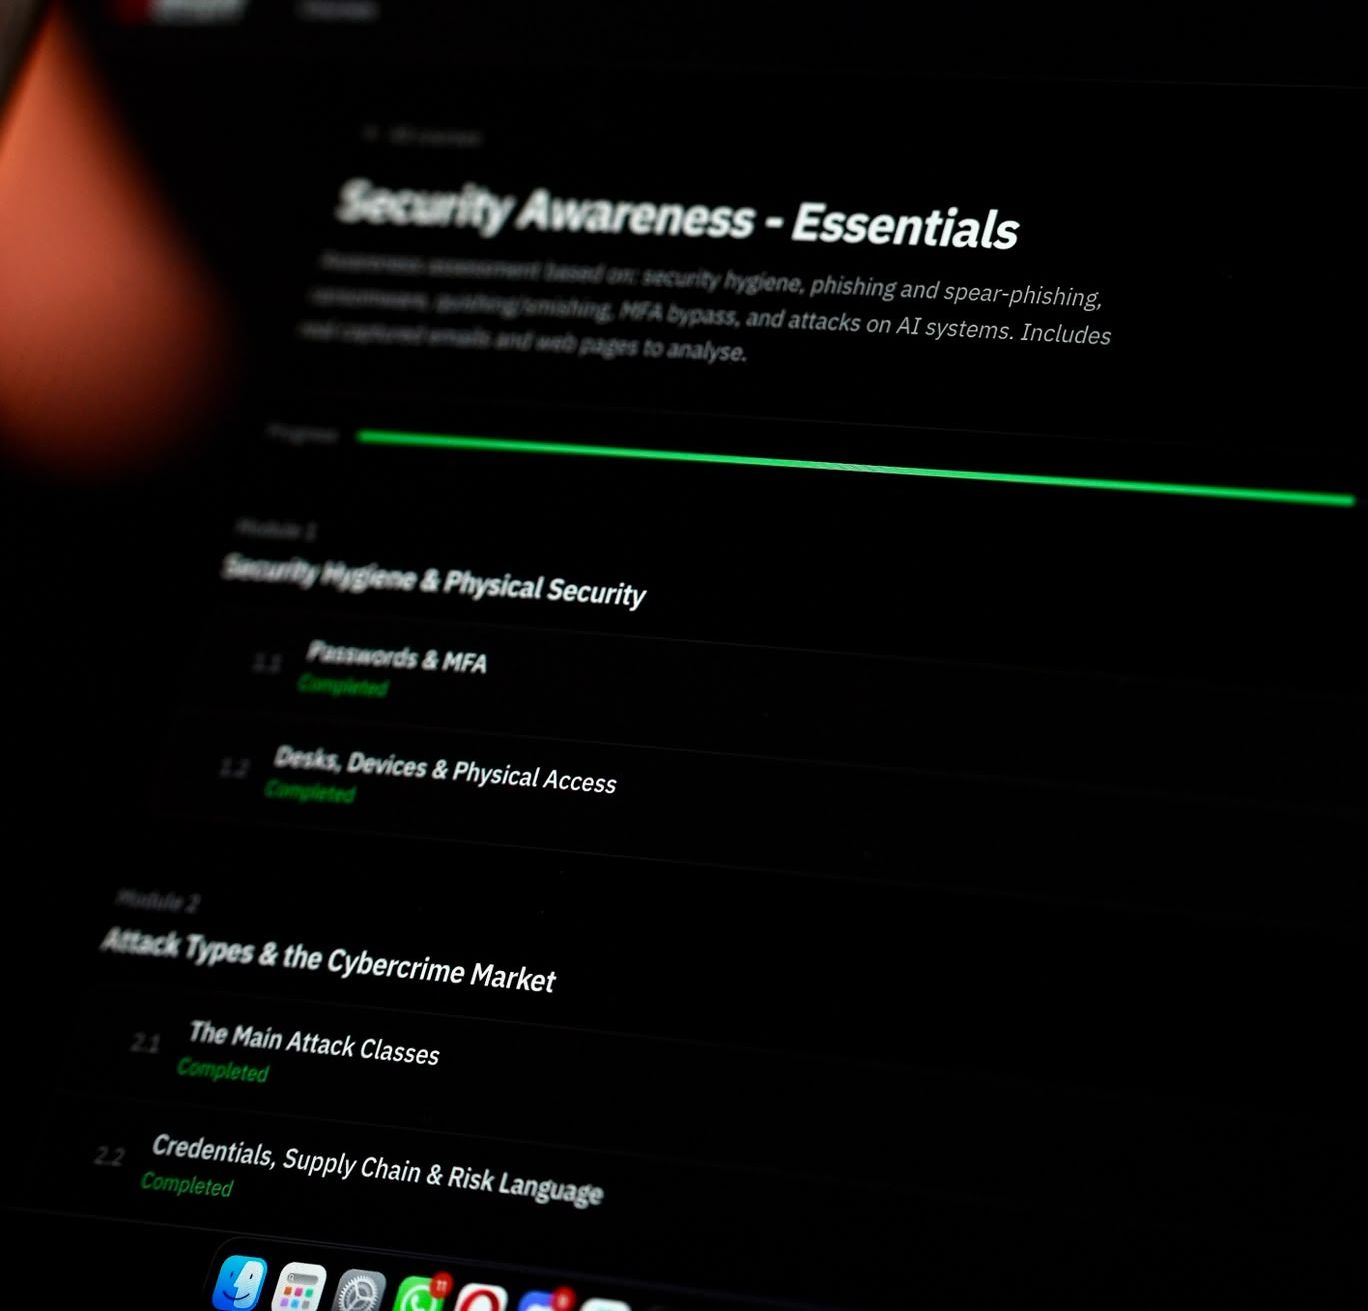
Course modules in the learner portal
03

Train users through interactive courses

Close the gap by educating learners through structured awareness content.

Built by professionals

Built by security professionals.

Our military-grade technologies provide the insight and operational advantage needed to detect and neutralize modern cyber threats.

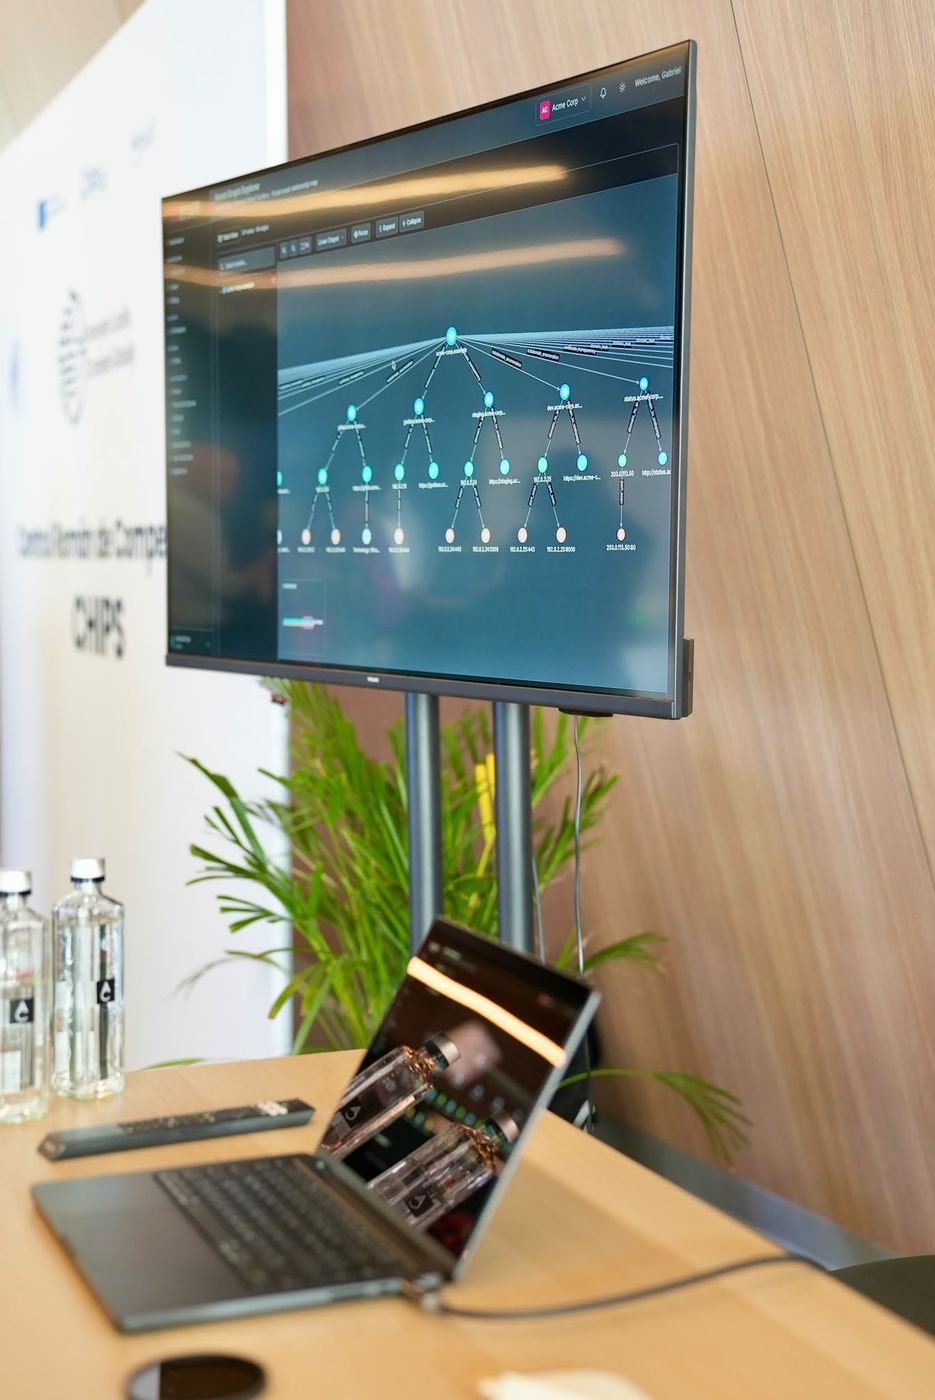
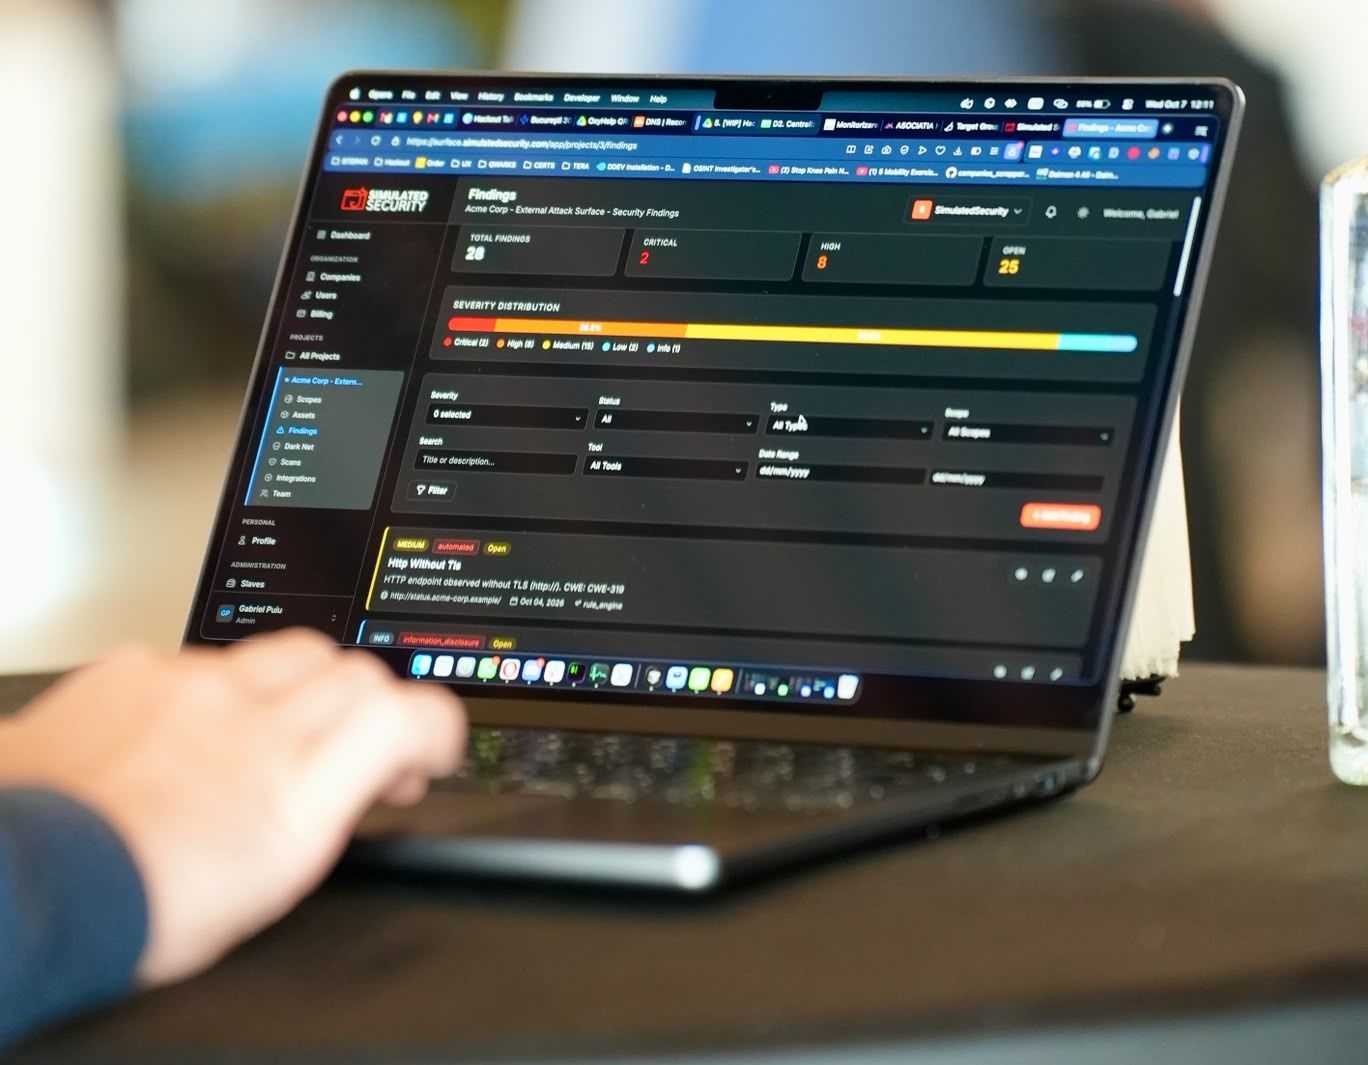
The asset graph on a large display at an event stand Two team members preparing a demo at the stand Security findings sorted by severity on a laptop

What clients say about Simulated Security

[REVIEWER NAME][ROLE · COMPANY]
★★★★★

[CLUTCH REVIEW QUOTE]

[REVIEWER NAME][ROLE · COMPANY]
★★★★★

[CLUTCH REVIEW QUOTE]

[REVIEWER NAME][ROLE · COMPANY]
★★★★★

[CLUTCH REVIEW QUOTE]

[REVIEWER NAME][ROLE · COMPANY]
★★★★★

[CLUTCH REVIEW QUOTE]

[REVIEWER NAME][ROLE · COMPANY]
★★★★★

[CLUTCH REVIEW QUOTE]

[REVIEWER NAME][ROLE · COMPANY]
★★★★★

[CLUTCH REVIEW QUOTE]

[REVIEWER NAME][ROLE · COMPANY]
★★★★★

[CLUTCH REVIEW QUOTE]

[REVIEWER NAME][ROLE · COMPANY]
★★★★★

[CLUTCH REVIEW QUOTE]

[REVIEWER NAME][ROLE · COMPANY]
★★★★★

[CLUTCH REVIEW QUOTE]

Integrations

Findings land where your team already works.

Built-in connectors, webhooks and an API-first approach for routing.

Jira Trello Slack Discord Email Wazuh Bugcrowd SIEM Webhooks API
/ 01

Less tool sprawl

External visibility, phishing simulation and training in one environment.

/ 02

Stronger workflows

Exposure discovery, human risk testing and awareness education, connected.

/ 03

Operational clarity

Manage multiple security initiatives without unnecessary complexity.

/ 04

Scalable adoption

Company-wide rollout designed for administrators and learners.

FAQ

Want a guided walkthrough?

We’ll tailor it to your environment.

Is this agentless?

Yes. Discovery and monitoring are designed to work without endpoint agents for fast deployment.

Can we integrate with Jira and SIEM?

Yes. Use built-in connectors, webhooks, and an API-first approach for routing.

How do you reduce noise?

Evidence-backed findings and scoring aligned to exposure, exploitability, and ownership signals.

Can we customize severity policies?

Yes. Map checks to your internal thresholds and enforce policies across business units.

Attacks are imminent. Are you ready?

Discover hidden weaknesses across your systems and team, simulate real-world threats, and train your staff.